
 Workforce Identity
 Endpoint Management
 Endpoint Detection & Response
 Vulnerability Management
 Compliance Automation
 Trust Center


Automate ISO 27701 readiness with adaptive compliance
For companies handling personal data at scale, ISO 27701 is how you prove privacy management rather than assert it. See how growing teams close the gap between running a privacy program and certifying it.
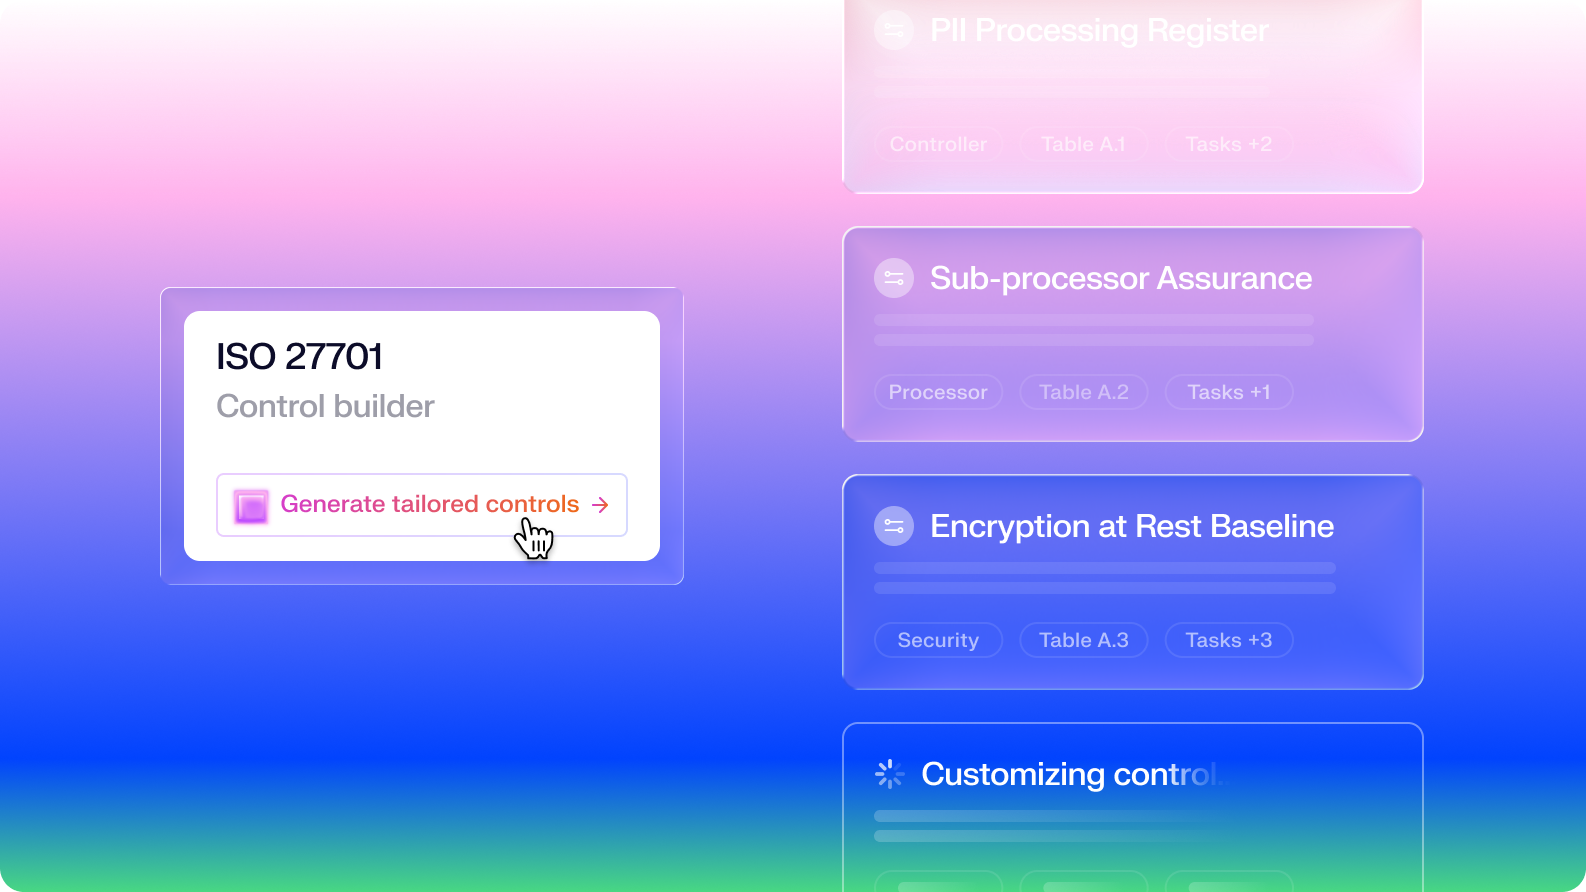
ISO 27701: Prove you manage privacy as a system
Unified by design. Built for the AI era.
Iru AI is designed from the ground up to connect a grid of agents behind the scenes—across identity, endpoint, and compliance. Powered by the Iru Context Model, it understands your users, apps, and devices to act safely, intelligently, and in context across your organization.
Iru combines native endpoint and identity telemetry with continuous evidence collection, making it easier to prepare for ISO 27701 certification and stay audit-ready all year.
Implement ISO 27701 controls, don't just document them
Iru's stack maps to Table A.3 — the information security controls that apply to controllers and processors alike. The controller and processor tables are privacy governance, and sit with your privacy team rather than your security team.
Automate evidence collection
Automatically pull evidence from connected sources via Iru Compliance Automation.Share compliance posture externally
Leverage a public-facing portal to share compliance posture via Iru Trust Center.Manage and secure devices
Iru Endpoint Management enforces device baselines, applies encryption, and maintains a live inventory of devices that processepersonal data.Secure worker access
Iru Workforce Identity replaces credentials with device-bound passkeys that evaluate device posture before granting access, and removes that access when needed.Keep software up to date
Iru Vulnerability Management gives you continuous visibility into operating system and third-party software risk, plus records that show controls operating.Contain cyber threats
Iru Endpoint Detection & Response contains threats in real time and generates the incident record your auditor will sample.Customize ISO 27701 controls for your unique business
Most compliance tools turn frameworks into generic checklists. Iru generates controls that are specific to your organization, in plain language, broken down into sub-tasks.
- Iru AI generates tailored controls, based on your company context and audit details
- You can migrate existing controls over from other products, or upload your own custom control set
- Controls become actions the moment they are created, with suggested owners and due dates
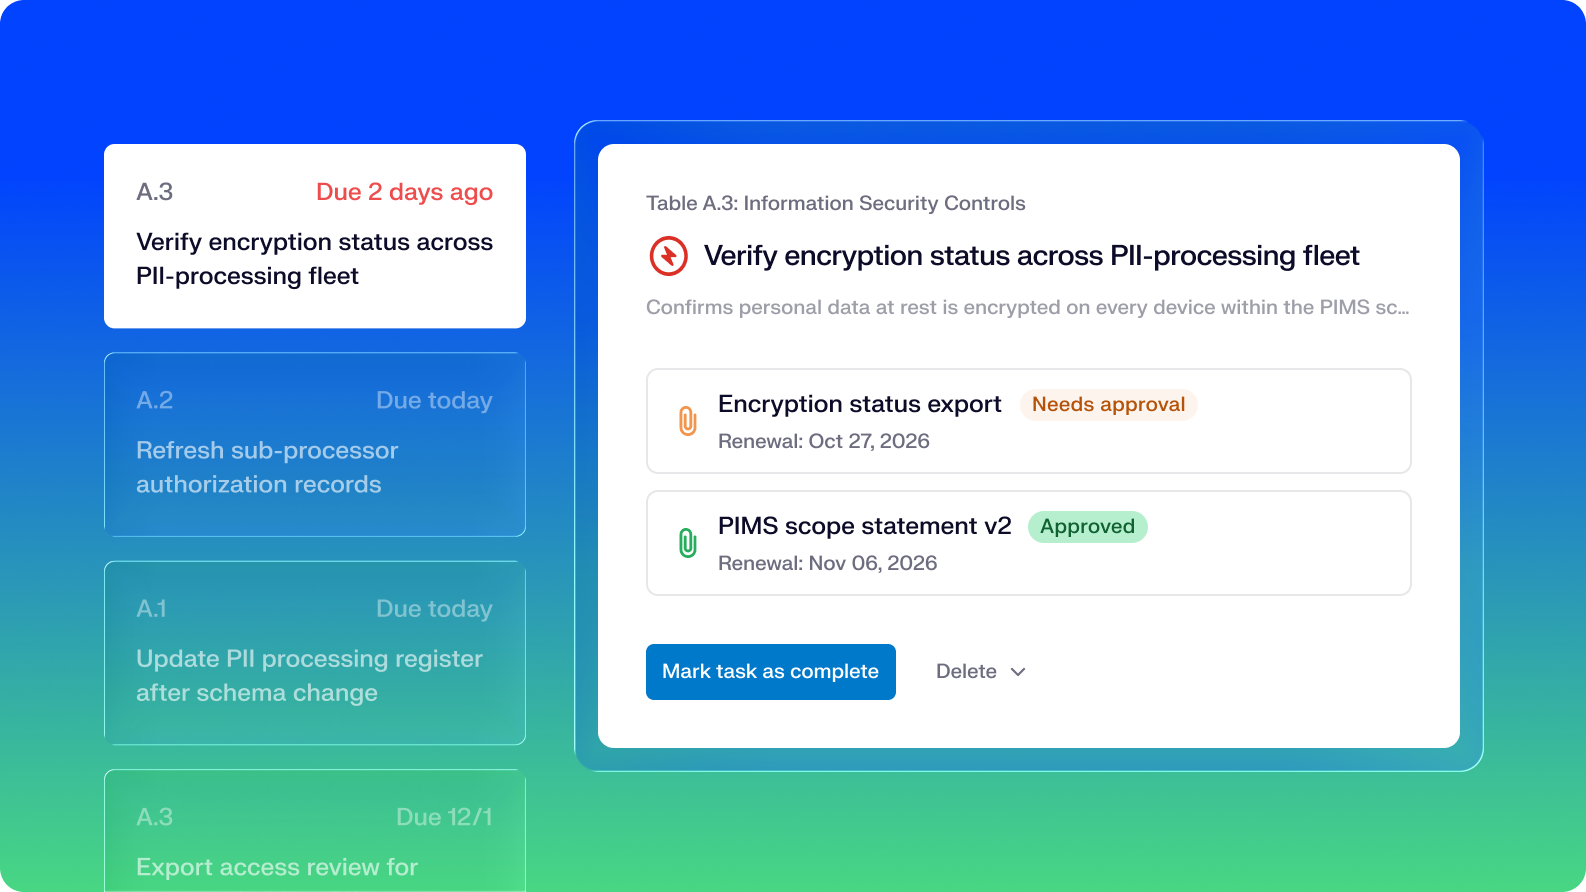
Automate your ISO 27701 evidence collection
For connected and activated sources, Iru can discover and attach relevant artifacts to the supported control actions, reducing manual uploads. And because you can manage your devices and identity within Iru, that data is pulled natively.
- Evidence flows in continuously from supported devices, integrations and systems
- Iru AI helps to identify stale, missing or potentially irrelevant evidence for you to review
- You stay better prepared before fieldwork begins, with fewer fire drills before your engagement
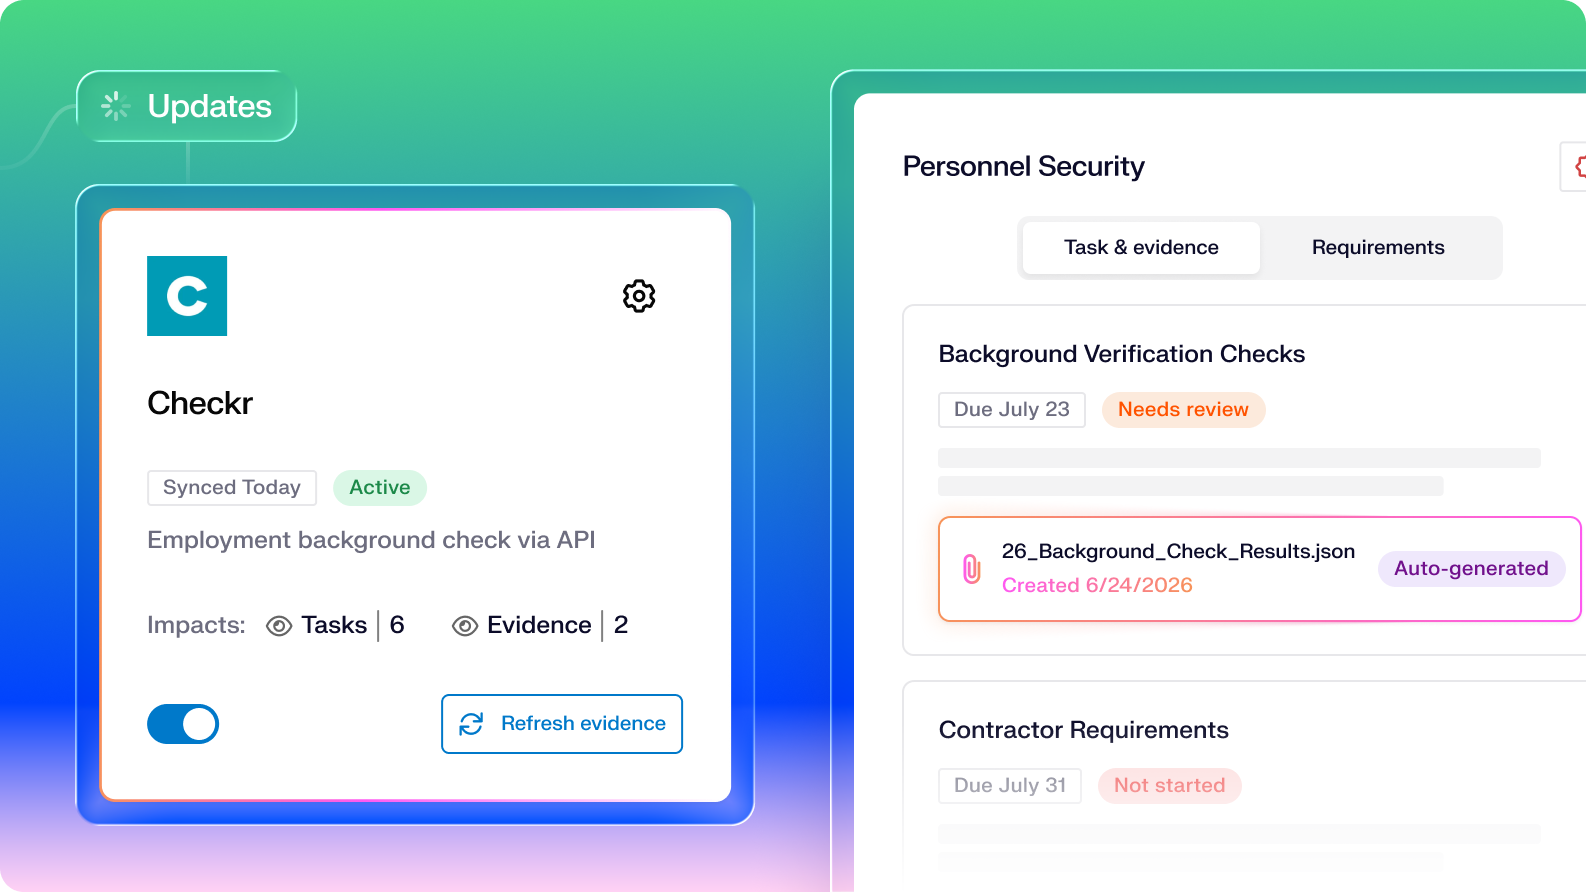
Ensure continuous ISO 27701 audit readiness
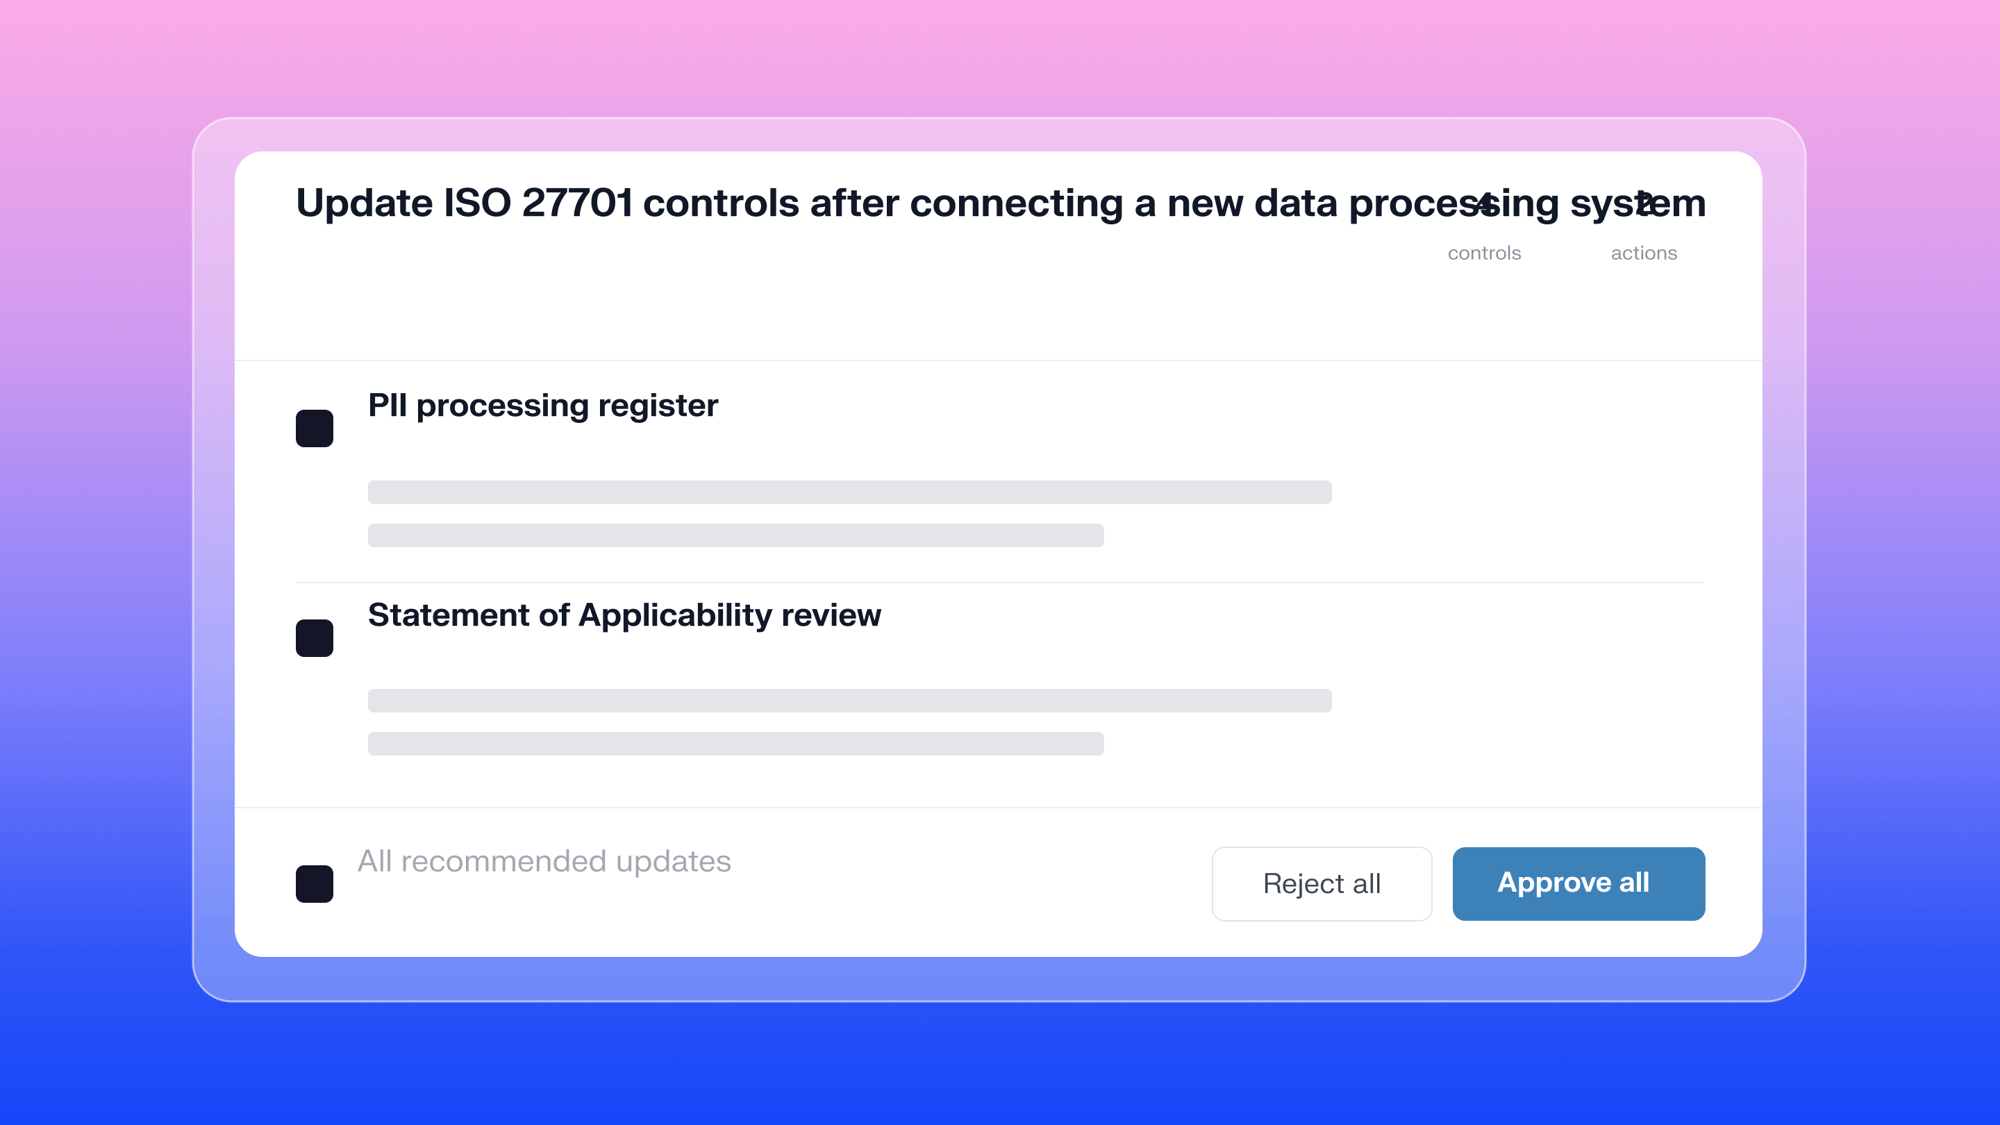
Iru's Adaptive Compliance capabilities watch for changes in your organization, and automatically suggest updates to your controls and actions.
- Iru AI regularly checks for changes to your sources, artifacts or company profile
- If a change is detected, a control update recommendation is surfaced for you to review, often within 24 hours
- No changes are made without your approval, and every change is logged for your auditors to review
Turn ISO 27701 preparation into an always-on workflow
Iru's AI-powered compliance solution helps IT, security and GRC teams spend less time on manual compliance work and stay audit-ready all year.
Let your team focus on what matters
Iru replaces fragmented tools with one AI-powered platform, so IT & security spend less time chasing tickets and more time improving the business.
Frequently asked
questions
Get answers to commonly asked questions
Who publishes and maintains ISO 27701 requirements?
ISO/IEC 27701 is published jointly by ISO and the IEC, developed by ISO/IEC JTC 1/SC 27 — the same subcommittee that owns ISO 27001. Certification is issued by independent certification bodies, accredited by national accreditation bodies such as UKAS and ANAB.
What does ISO 27701 evaluate?
Whether you run a privacy information management system — a PIMS. It sets requirements for establishing, implementing, maintaining, and continually improving one, and it's designed for organizations acting as PII controllers, PII processors, or both.
Which role you're in matters. The annex separates controls that apply to controllers from those that apply to processors, with a third set of information security controls applying to both.
Is ISO 27701 still an extension of ISO 27001?
No, not since the 2025 edition. The 2019 version was formally an extension to ISO 27001 and 27002, which meant you couldn't certify to it without an ISO 27001 ISMS underneath.
ISO/IEC 27701:2025 converted PIMS into a standalone management system standard. ISO states it plainly: asked whether 27701 can be used alone, their answer is "Yes, as it is an independent management system standard."
ISO 27001 still helps. The two share the same harmonized structure, and ISO notes that 27701 "aligns with existing ISO/IEC 27001 systems to streamline implementation." It's now an accelerator rather than a prerequisite.
Importantly, many certification bodies will run a combined ISO 27001 + ISO 27701 audit.
What changed in the 2025 edition?
Six things were adjusted:
- PIMS became a standalone management system standard
- The latest harmonized structure was adopted
- Leadership, governance and performance evaluation requirements were strengthened
- Climate change considerations were introduced
- Privacy risk management was formally embedded in the management system
- The controller and processor controls were restructured and clarified.
The restructuring is the one with practical consequences. The old Annex A (controller) and Annex B (processor) split has been replaced by three tables: controller controls, processor controls, and information security controls applying to both.
Published 14 October 2025, alongside ISO/IEC 27706:2025 — the standard governing bodies that audit and certify PIMS.
Our certificate is against ISO 27701:2019. Is it still valid?
For now. The 2019 edition has been withdrawn, but existing certificates issued against it run to 31 October 2028. After that they expire.
What does the transition involve?
Less than you might expect. It doesn't require a separate audit — you can transition at a surveillance or recertification visit. The transition audit does not restart your certification cycle or move your expiry date, and it is roughly half a day of extra auditor time.
What you need going in: updated documentation, a rebuilt Statement of Applicability, and an internal audit covering the new requirements.
Is there a Statement of Applicability?
Yes, and it's still required.
If you're transitioning from 2019, note that it has to be rebuilt rather than edited. The controls have been redistributed across the annex's three tables, so your old clause references won't map across cleanly. Budget time for this — it's the part of the transition people underestimate.
Do we have to implement every control in the annex?
No. The annex is a reference set, not a checklist.
As with ISO 27001, you determine the controls your risk treatment actually requires, then compare that set against the annex to confirm nothing necessary was left out. The result goes in your Statement of Applicability: what applies, why, whether it's implemented, and your justification for anything excluded.
Which table applies to you depends on your role. A pure processor isn't assessed against the controller controls. You can, however, be both, and thusly both tables will apply to your organization.
Can we get certified to ISO 27701:2025 today?
Yes, accredited certification is available, but the pool of certification bodies is still small.
Accreditation bodies began assessing certification bodies for the 2025 edition in 2026, and some were accredited earlier. Before you sign, check the certification body's accreditation scope and which accreditation body granted it. Not every body offering PIMS certification is accredited for the 2025 edition yet, and a certificate from one that isn't may be worth considerably less to a buyer.
How long does certification take?
No official benchmark exists, so treat any number as an estimate.
If you already run a mature ISO 27001 ISMS, roughly 3 to 6 months to Stage 2. From a standing start, 6 to 12 months. Where you land depends on your scope, your maturity, and your size.
One hard constraint regardless: an internal audit and a management review must have run before Stage 2. You can't certify a management system that started last week, however fast you implement.
Does ISO 27701 make us GDPR compliant?
No, and be careful with anyone who implies it does.
ISO lists among the standard's benefits that it "helps demonstrate compliance with global privacy regulations such as GDPR." That's supporting evidence, not a substitute. GDPR compliance depends on your lawful bases, your processing activities, your contracts, and decisions no certification confers — and GDPR itself is explicit that certification doesn't reduce your responsibility for compliance.
Treat a PIMS certificate as strong evidence of privacy management maturity, which is genuinely useful in a security review. It is not an answer to the Regulation.
Can Iru certify us, or issue an ISO 27701 certificate?
No compliance software can issue an ISO 27701 certificate. Certification must come from an independent certification body, accredited by a recognized accreditation body — that independence is the entire basis of the certificate's value.
Our platform acts as the engine room. It connects to your systems, gathers evidence continuously, manages your policies and Statement of Applicability, and hands your auditor an organized package instead of a scramble.
If you would like to work with one of the certification bodies we partner with, please book a demo to explore the compliance solution. Existing customers can reach out to their rep for info about our audit partners.