
 Workforce Identity
 Endpoint Management
 Endpoint Detection & Response
 Vulnerability Management
 Compliance Automation
 Trust Center



Adaptive integrations
Integrations are continuously adaptive, pulling in the most relevant evidence based on actual control language.
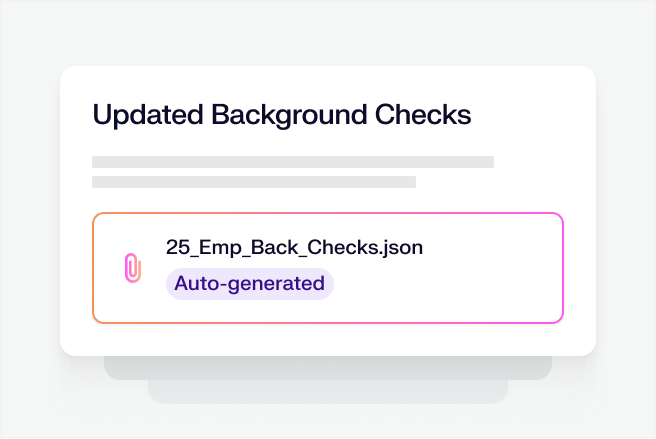
Artifact relevancy
Iru AI validates evidence, maps it to the correct controls, and flags anything irrelevant or stale using its Adaptive Evidence Map.

Collaborative tasks
Each control becomes actionable tasks with owners and due dates. Collaborate in comments, attach evidence, and track progress in one place.
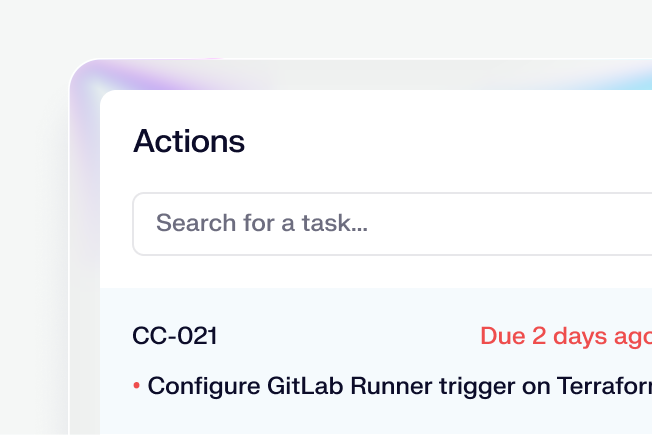
Compliance inbox
Personal to-do lists give team members a view of their assigned tasks, allowing for delegation, comments, and history.
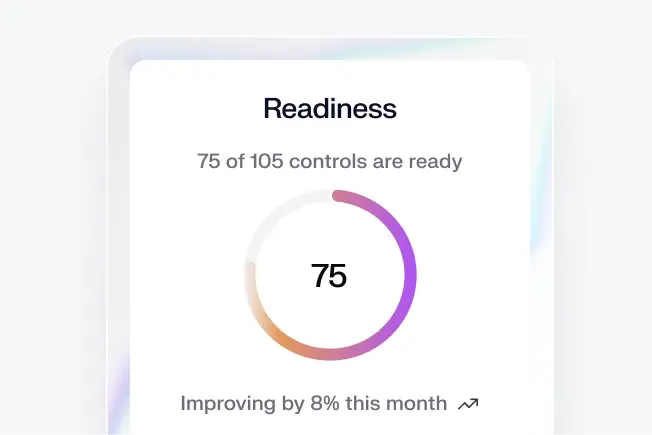
Continuous progress tracking
See controls, tasks, evidence, and frameworks update in real time—know exactly where you stand with no surprises.

Auditor validation
Evidence lives under each control with dynamic summaries, lineage, and timestamps, so auditors can verify fast and move on.
Trust Center publishing
Share certifications, audit results, and security posture in a public Trust Center to help sales move faster.

Questionnaire agent
Iru AI drafts responses to security questionnaires, pulling data directly from the Adaptive Evidence Map.
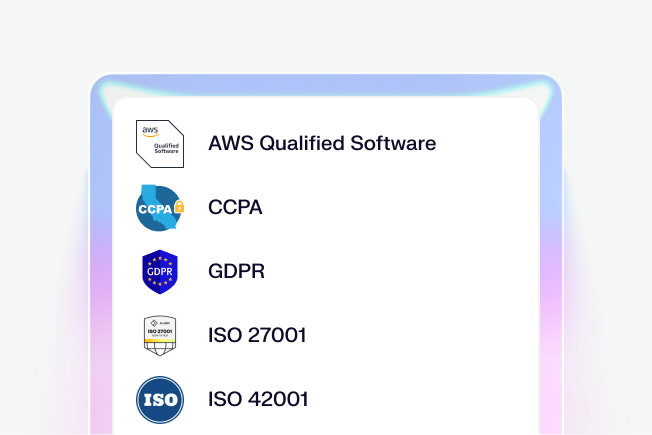
KPI dashboard
Showcase the security controls you have in place and the frameworks you comply with to build trust at a glance.
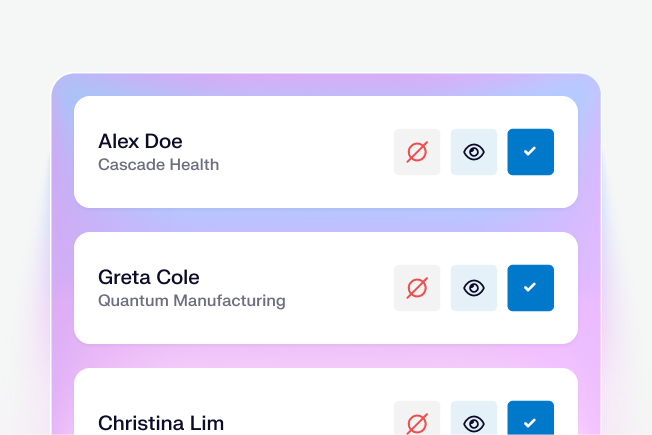
NDA verification
Ask prospects to sign NDAs before downloading sensitive documents. Iru AI verifies signed NDAs and a human in the loop gives final approval to access the private portal.
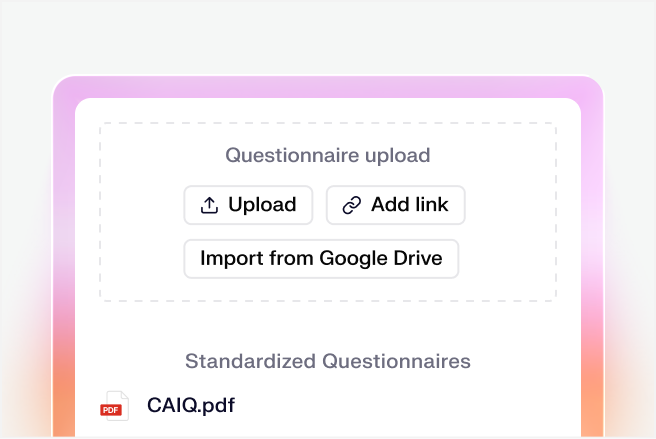
Questionnaire submissions
Allow security and procurement teams to upload their own questionnaires for your input. Uploaded files feed into Iru AI for draft answers and fast turnarounds.
Branding
Make your public page match your brand with custom domain, colors, logo, and company description.
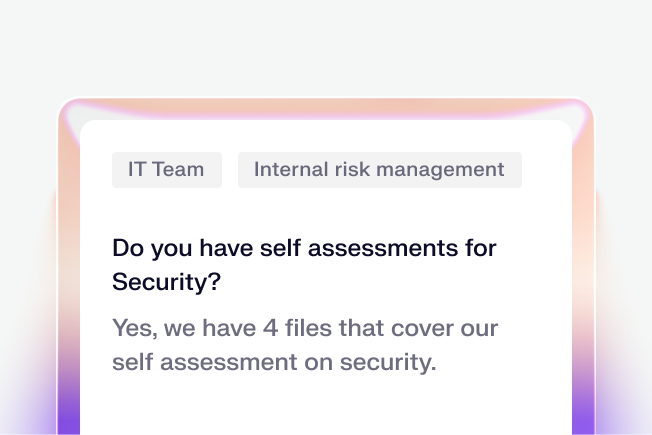
Public FAQs
Answer the most commonly asked questions during procurement. Metadata helps with sorting and tagging at any scale.