Skip to content
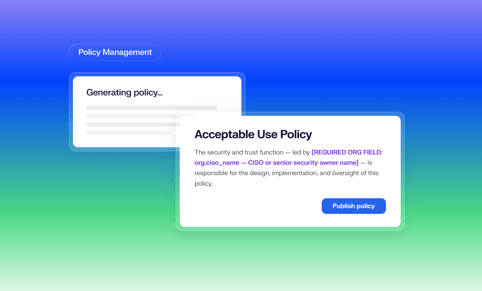
Introducing Policy Management: Create, publish and track compliance policies in Iru
Pedro Ventura

5 min read

Introducing Policy Management: Create, publish and track compliance policies in Iru

It's Thursday afternoon. The audit is in 45 days.

Product News
Compliance Automation momentum: new frameworks and industry recognition
Iru Team

4 min read

Compliance Automation momentum: new frameworks and industry recognition

As of this week, Iru Compliance Automation supports three new frameworks: CMMC, NIST SP 800-171, and ISO 27701. These frameworks join the others within Iru Compliance Automation today (SOC 2, ISO 27001, ISO 42001, GDPR, HIPAA, NIST 800-53, and NIST CSF 2.0), bringing the total to ten.

Product News
What is endpoint visibility and control, and how does it work?
Iru Team

8 min read

What is endpoint visibility and control, and how does it work?

Endpoint visibility gives you a real-time view of your endpoints, including device inventory, patch status, configurations, running processes, and security posture. Your new list iEndpoint control lets you act on that data by deploying patches, enforcing policies, restricting software, and remediating threats.tem Endpoint visibility and control combines monitoring and remediation, helping you identify risks and fix them from a single platform. Visibility without control creates security gaps since detecting issues is only half the job. The ability to remediate them quickly is what reduces risk. Features like automated patching, policy enforcement, and continuous compliance help reduce manual work and keep your endpoints secure. Every endpoint tells a story. One laptop is missing critical patches. Another is running unauthorized software. A contractor's device hasn't checked in for weeks. You know exactly what's happening across your environment, but knowing isn't the same as fixing.

Managed OS for Windows: Enforce updates on your timeline
Lance Crandall

2 min read

Managed OS for Windows: Enforce updates on your timeline

Target a Windows feature release, set a deadline, and know that devices will be running that version when it arrives.

Product News
Config as Code for device management: How it works in Iru
Mike Boylan

9 min read

Config as Code for device management: How it works in Iru

Most device management workflows still depend on tribal knowledge. An admin makes a change, documents it somewhere (maybe), and hopes the next person understands why it was done. At small scale, that’s manageable. At enterprise scale, it’s a risk.

Product News
How to automate Mac patch management with Iru in 3 simple steps
Iru Team

10 min read

How to automate Mac patch management with Iru in 3 simple steps

Educational
WWDC 2026: The declarative era is here
Iru Team

4 min read

WWDC 2026: The declarative era is here

Apple just removed the legacy MDM commands for software update management. As of OS 27, not deprecated with a long runway, not flagged as discouraged, they’re gone. That's a clear signal yet that the declarative era is here.

Educational
Apple's next operating systems: How and why to test them now
Arek Dreyer

14 min read

Apple's next operating systems: How and why to test them now

We say it every year at this time: Now that Apple’s beta software programs for its next operating systems are open, it’s time for you as an Apple admin to begin testing them. The earlier you test, the more time you give Apple to fix the problems you report.

Educational
Introducing Adaptive Compliance: Your controls stay current, automatically
Pedro Ventura

5 min read

Introducing Adaptive Compliance: Your controls stay current, automatically

Iru AI watches how your organization changes. Your compliance program keeps up.

Product News
Mac MDMs: How to Manage and Secure Your Device Fleet
Iru Team

11 min read

Mac MDMs: How to Manage and Secure Your Device Fleet

Mac mobile device management (MDM) is a framework that lets IT administrators remotely set up, manage, and secure Apple devices from a single place. When a device is enrolled, it receives a profile that builds a channel between the device and the MDM server. When IT applies a policy or issues a command in the MDM console, the software sends a notification to the device, which retrieves the information and applies it locally. Businesses use Mac MDM to automate device onboarding, enforce company security policies, deploy apps and updates, and maintain compliance, all without needing to physically engage with the device.

Endpoint Drift: Why EDR coverage breaks down at scale [+ Take the quiz to see where you stand]
Iru Team

7 min read

Endpoint Drift: Why EDR coverage breaks down at scale [+ Take the quiz to see where you stand]

Your dashboard says every endpoint is covered. Patches show as deployed. Policies look locked down.

Educational
Inside SStar Agent, a cross-platform RAT with an unfinished macOS toolkit
Adam Kohler

Calvin So

19 min read

Inside SStar Agent, a cross-platform RAT with an unfinished macOS toolkit

Threat Intelligence
Enroll Windows devices automatically through Autopilot
Lance Crandall

2 min read

Enroll Windows devices automatically through Autopilot

Setting up a new Windows device used to mean manual imaging and IT getting their hands on hardware, and many teams are still doing it this way. Windows Autopilot offers a better path: zero-touch deployment where devices ship direct from the vendor and enroll the moment the employee signs in for the first time. Iru connects directly to that flow, so the setup you configure once applies to every device.

Product News
NVD's shift to risk-based prioritization: how Iru Vulnerability Management stays ahead of the limitations
Shwena Kak

6 min read

NVD's shift to risk-based prioritization: how Iru Vulnerability Management stays ahead of the limitations

NIST formally transitioned the National Vulnerability Database to a risk-based enrichment model in April 2026, meaning only CVEs that meet specific criteria, like those in CISA's KEV catalog or affecting federal software, will be prioritized for enrichment. Everything else gets deferred. This leaves a significant gap for security teams that depend on NVD data for vulnerability management. Iru VM was built to operate independently of NVD's limitations, drawing from multiple sources and providing its own human-in-the-loop enrichment. To date, Iru's Security Research team has enriched close to 2,000 CVEs and corrected around 170 inaccurate NVD records, with 66% of all vulnerability detections across customer endpoints driven by Iru-enriched data. The CVE program has long been a vital part of vulnerability intelligence and protecting critical infrastructure. For the past couple of decades, the National Vulnerability Database (NVD), run by NIST, has served as a foundational reference for vulnerability intelligence, providing severity scores, product metadata, and structured enrichment that security teams and tooling depend on every day.


Threat Intelligence
How to build a tech stack that runs itself
Iru Team

5 min read

How to build a tech stack that runs itself

Gorilla's IT lead shares the playbook he uses to automate onboarding, offboarding, and compliance with Iru so routine work runs itself and the team can focus on higher-value projects. IT teams are being asked to do more than ever. Device management, security, compliance, AI enablement, and often all of it with a team of one. The difference between keeping up and falling behind often comes down to how much of the routine work can run without you.

Educational

Stay up to date

Iru's bi-weekly collection of articles, videos, and research to keep IT & Security teams ahead of the curve.