Skip to content

Reliable Windows app patching with Iru system tray notifications

Lance Crandall Lance Crandall
Reliable Windows app patching with Iru system tray notifications

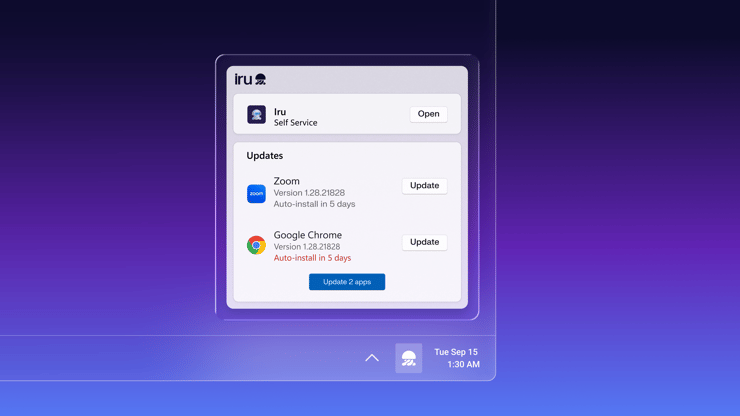
Notify Windows users when app updates are available. When your users are ready, they can allow Iru to close the app and update the application. Employees get more control over when updates land, and you spend less time chasing down unpatched devices.

Vendors regularly release application updates without notice, and keeping endpoints secure requires patches to land quickly across the entire fleet. However, deployment is often delayed because applications must be closed before updates can take effect.

It happens all the time: an employee leaves primary software running for days, causing background MDM patches to repeatedly fail.

Now, you have to forcibly close active applications, disrupt daily work, and play the villain. So, how do you automate application updates reliably without impairing daily productivity?


Predictability over when patches land

When there is an update to either an Auto App or a Custom app, Iru’s endpoint agent will actively look to install app updates silently every 15 minutes. If the app update fails, pending updates appear in Iru’s system tray application on employee devices. From here, employees will be prompted every 8 hours if pending app updates are still available.

Alongside the update notification, employees will see an enforcement deadline. When the deadline is reached, Iru will close the app and proceed with the update ensuring the device is patched.

As a result, IT admins gain the trust that app updates will land on devices by the scheduled enforcement deadline.

Employees decide what apps to update and when

Pending updates in the system tray application give employees control over when they want to update their applications, whether a single update or all at once. For example, if an employee has a Zoom presentation in 5 minutes, they don't have to risk updating Zoom right now. They can update just Slack or Excel, get their work done, and handle Zoom later when their schedule is clear.

When employees reach the deadline, a prompt with a 5-minute countdown will appear. Users will be able to delay up to an additional, cumulative 24 hours. At this point, Iru will close the app and proceed with the update ensuring the device is patched.

Predictable compliance without user friction

Every IT team knows the difficulty of ensuring devices are secure and compliant. Iru’s Window’s system tray application now engages employees in the app patching process, giving them control over when updates land. As a result, IT gets more predictable patch compliance within the enforcement window.

Take the headache out of application updates. Book a demo to see Iru’s system tray app in action.

Recent Articles

Featured image: Rustbot, the macOS malware used in the latest Rust Supply Chain Attack
Cristian Molina 10 min read

Rustbot, the macOS malware used in the latest Rust Supply Chain Attack

On August 20, 2026, attackers published malicious versions of three widely used Rust packages to crates.io, the official Rust package registry. On macOS, the payload is a remote access trojan (RAT) that collects cloud credentials, SSH keys, cryptocurrency wallet data, and browser profile information, then sends it to attacker-controlled infrastructure. It installs a launch agent to survive reboots and accepts follow-on commands from its operators. Once running, it decrypts its configuration, profiles the host, Reads the local browser stores, installs persistence via LaunchAgent, and beacons out. The packages were available for approximately two hours before removal. The attackers also withdrew the previous stable versions, which pushed automated dependency resolution toward the compromised releases. Any environment that compiled an affected project during that window should be treated as compromised. This blog documents Iru's analysis of the native Apple Silicon ARM64 implant.
Threat Intelligence
Featured image: Inside the screensharingd Bugs: How macOS Screen Sharing Went from Root File Access to Pre-Auth Compromise
Csaba Fitzl 6 min read

Inside the screensharingd Bugs: How macOS Screen Sharing Went from Root File Access to Pre-Auth Compromise

In late July 2026, a cluster of vulnerabilities in macOS Screen Sharing turned what initially looked like a fairly constrained privilege problem into one of the more interesting macOS remote-attack stories in years.
Threat Intelligence
Featured image: Apple is deprecating hdiutil in macOS 27 Golden Gate. Are your scripts ready?
Arek Dreyer 3 min read

Apple is deprecating hdiutil in macOS 27 Golden Gate. Are your scripts ready?

If you spent part of last weekend fielding Slack messages about hdiutil, you're not alone. Jeff Johnson's lapcatsoftware.com blog flagged that the man page for hdiutil in the macOS 27 Golden Gate beta now carries a deprecation notice:

Educational

See Iru in action

Discover why thousands of teams choose Iru

By submitting this form I agree to Iru’s Privacy Policy and consent to be contacted by Iru about its products and services.

Stay up to date

Iru's bi-weekly collection of articles, videos, and research to keep IT & Security teams ahead of the curve.