Skip to content

Automate NIST 800-171 readiness with adaptive compliance

For contractors handling Controlled Unclassified Information (CUI), NIST 800-171 is the baseline your contract depends on. See how growing teams close the gap between implementing the requirements and evidencing them.

ISO 27701 Controls-1

NIST 800-171: Prove you protect CUI, continuously

Unified by design. Built for the AI era.

Iru AI is designed from the ground up to connect a grid of agents behind the scenes—across identity, endpoint, and compliance. Powered by the Iru Context Model, it understands your users, apps, and devices to act safely, intelligently, and in context across your organization.

Iru combines native endpoint and identity telemetry with continuous evidence collection, making it easier to implement the technical requirements of NIST 800-171 and keep your assessment evidence current.

Implement NIST 800-171 controls, don't just document them

Full Iru platform vs standalone compliance tools
Iru
Standalone compliance tools

Automate evidence collection

Automatically pull evidence from connected sources via Iru Compliance Automation — Security Assessment

Answer prime contractor questionnaires

Share your security posture through a public-facing portal via Iru Trust Center

Control access to CUI

Device-bound multi-factor authentication and separated admin accounts via Iru Workforce Identity — Access Control, Identification and Authentication

Encrypt CUI at rest

Apply full-disk encryption and maintain a live record of protected devices via Iru Endpoint Management — Media Protection

Maintain secure configuration

Enforce secure baselines across your fleet via Iru Endpoint Management — Configuration Management

Keep software patched

Continuously detect and remediate OS and third-party software risk via Iru Vulnerability Management — System and Information Integrity

Detect and respond to incidents

Contain threats and document what happened via Iru Endpoint Detection & Response — Incident Response

Control media and device disposal

Govern secure disposal and reuse of devices that held CUI via Iru Endpoint Management — Media Protection
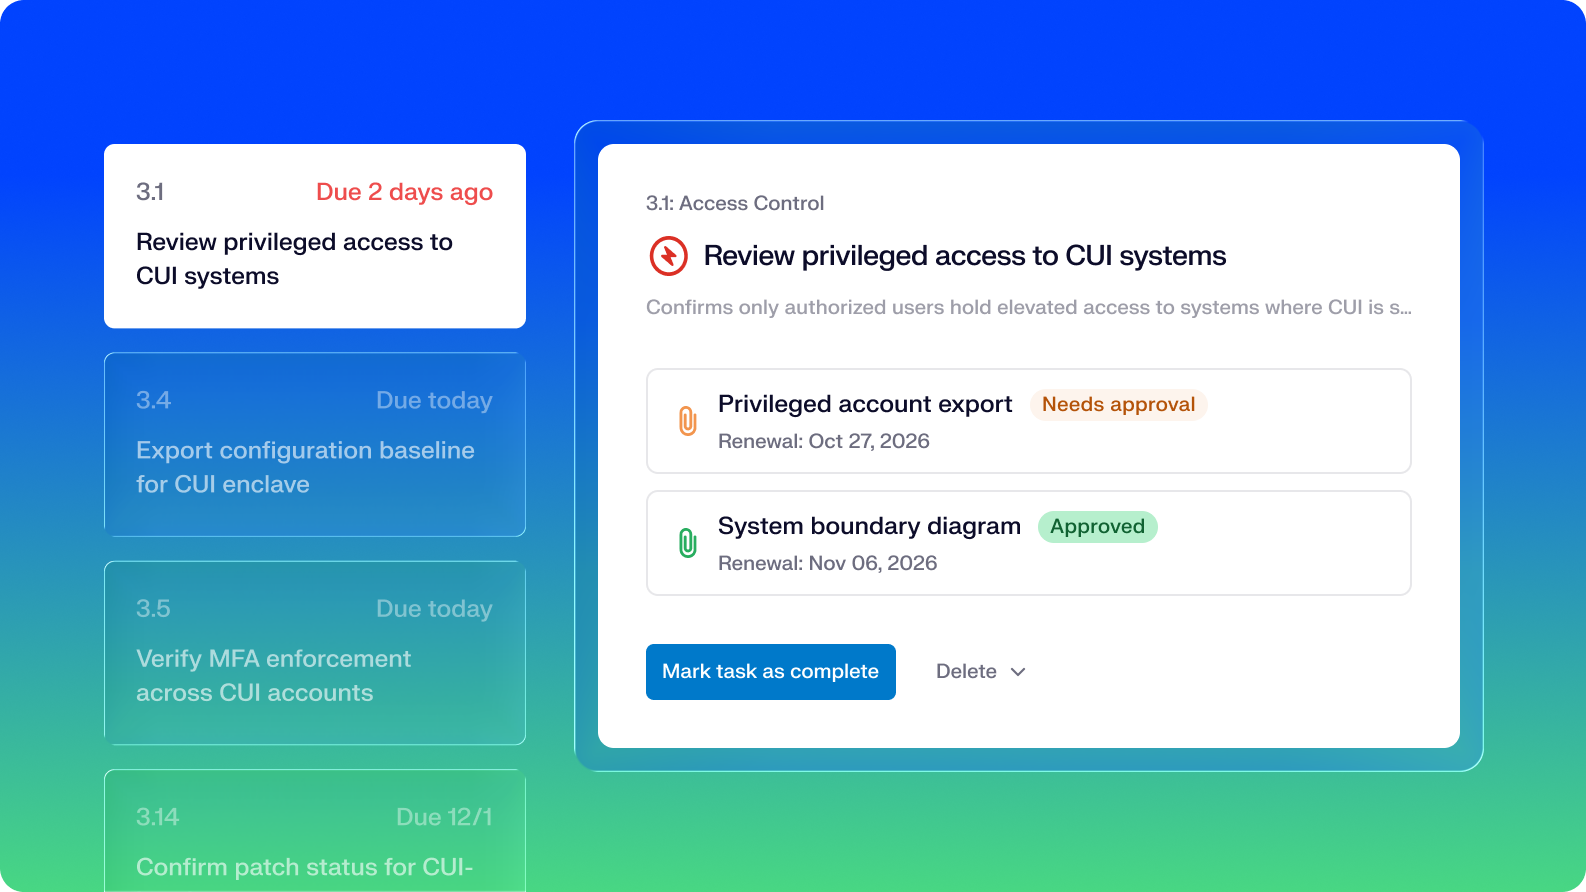
Customize NIST 800-171 controls for your unique business

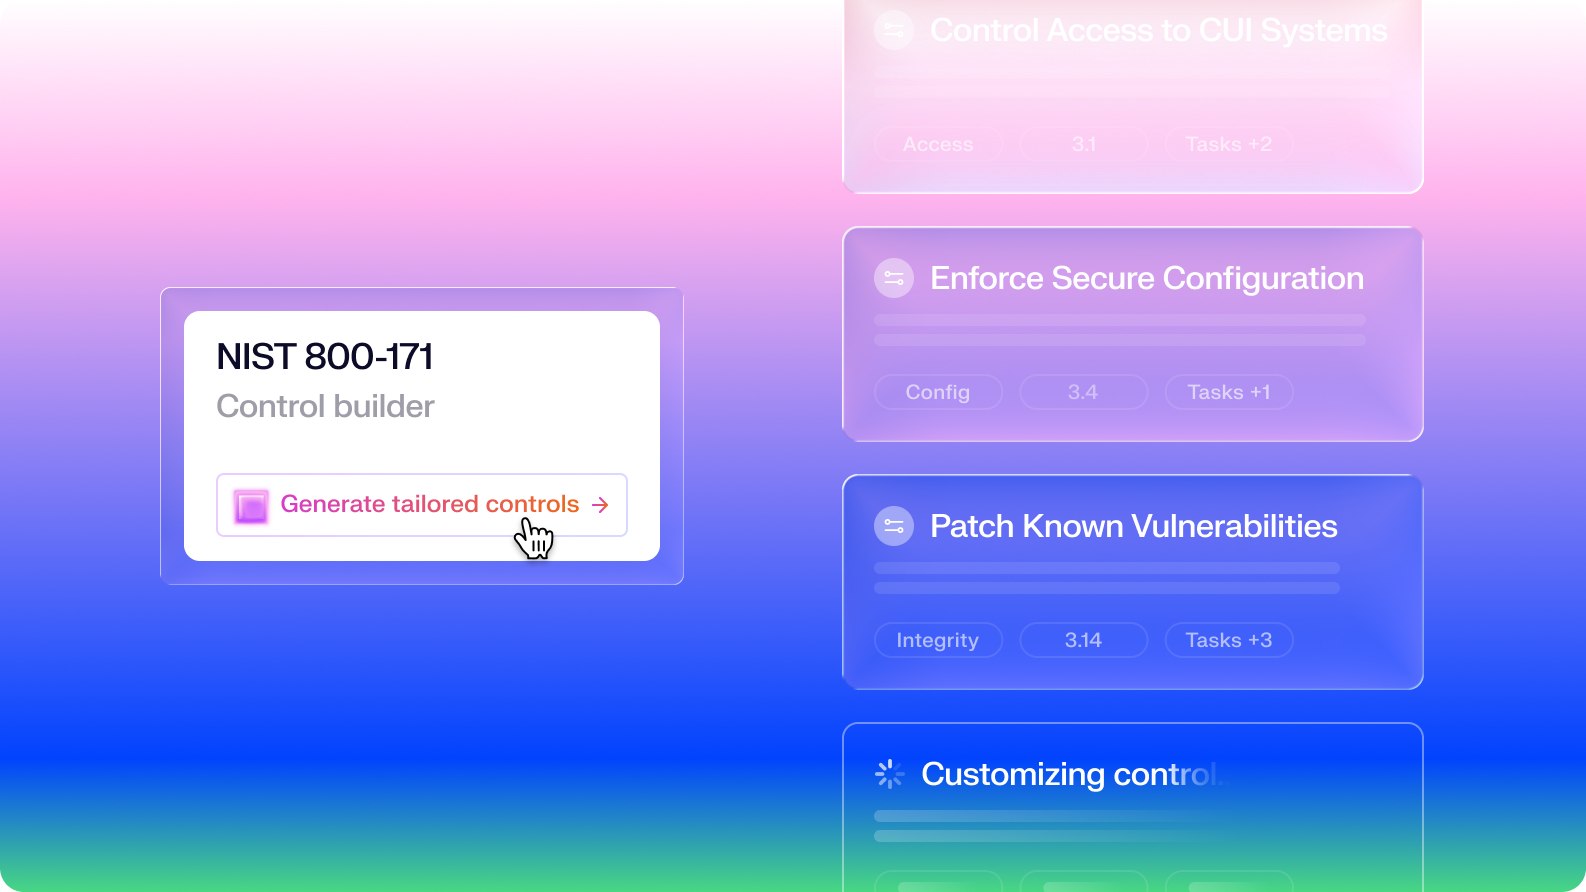
Most compliance tools turn frameworks into generic checklists. Iru generates controls that are specific to your organization, in plain language, broken down into sub-tasks.

  • Iru AI generates tailored controls, based on your company context and audit details
  • You can migrate existing controls over from other products, or upload your own custom control set
  • Controls become actions the moment they are created, with suggested owners and due dates
NIST 800-171 Actions

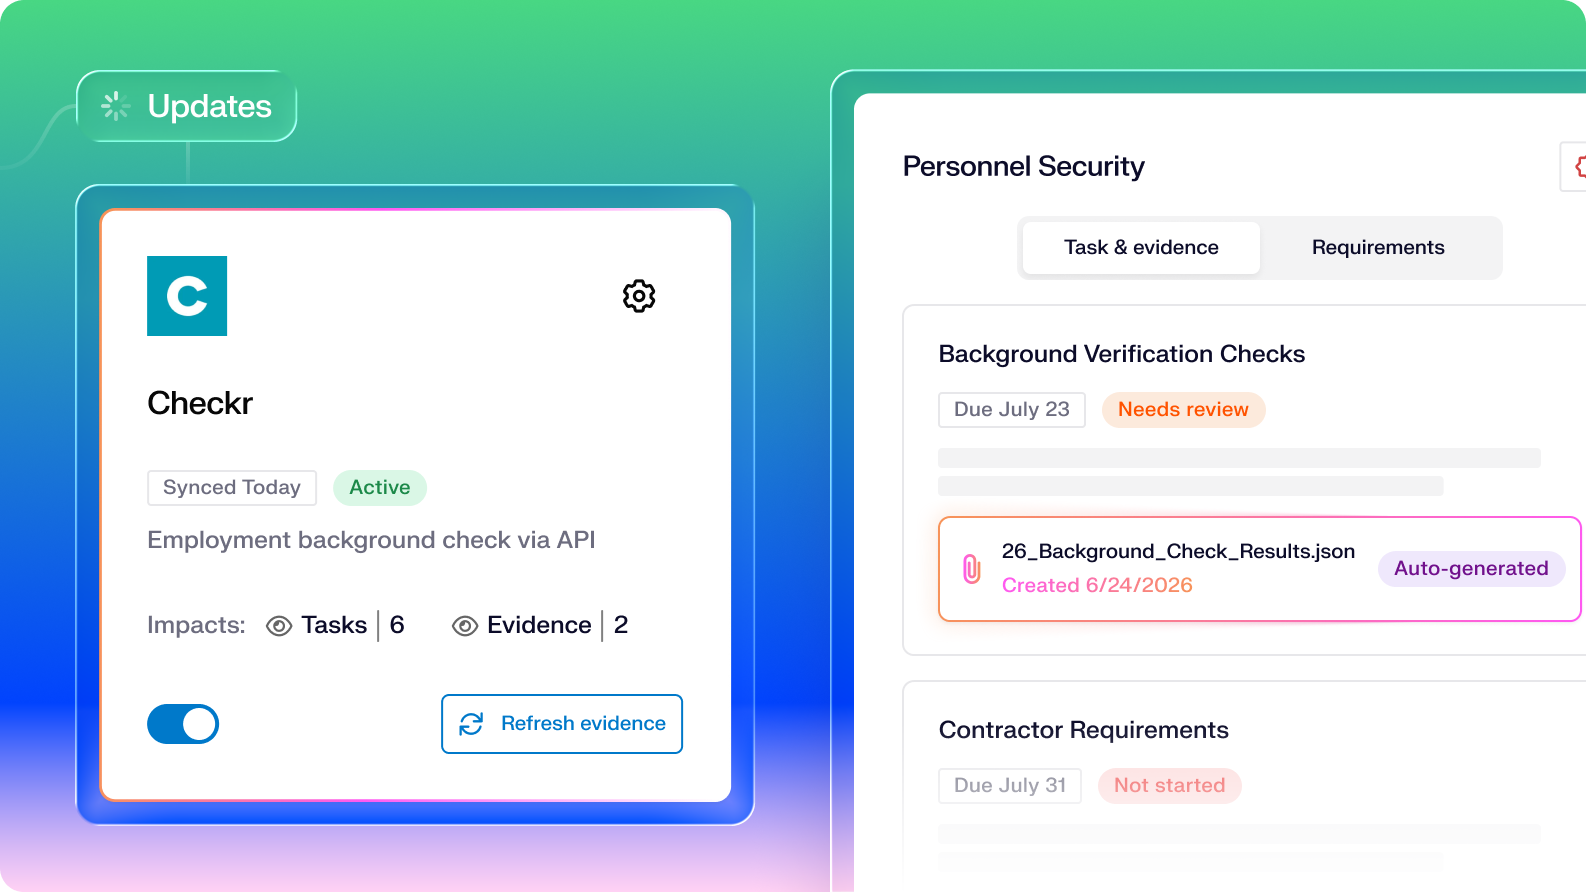
Automate your NIST 800-171 evidence collection

For connected and activated sources, Iru can discover and attach relevant artifacts to the supported control actions, reducing manual uploads. And because you can manage your devices and identity within Iru, that data is pulled natively.

  • Evidence flows in continuously from supported devices, integrations and systems
  • Iru AI helps to identify stale, missing or potentially irrelevant evidence for you to review
  • You stay better prepared before fieldwork begins, with fewer fire drills before your engagement
ISO 27701 evidence

Ensure continuous NIST 800-171 audit readiness

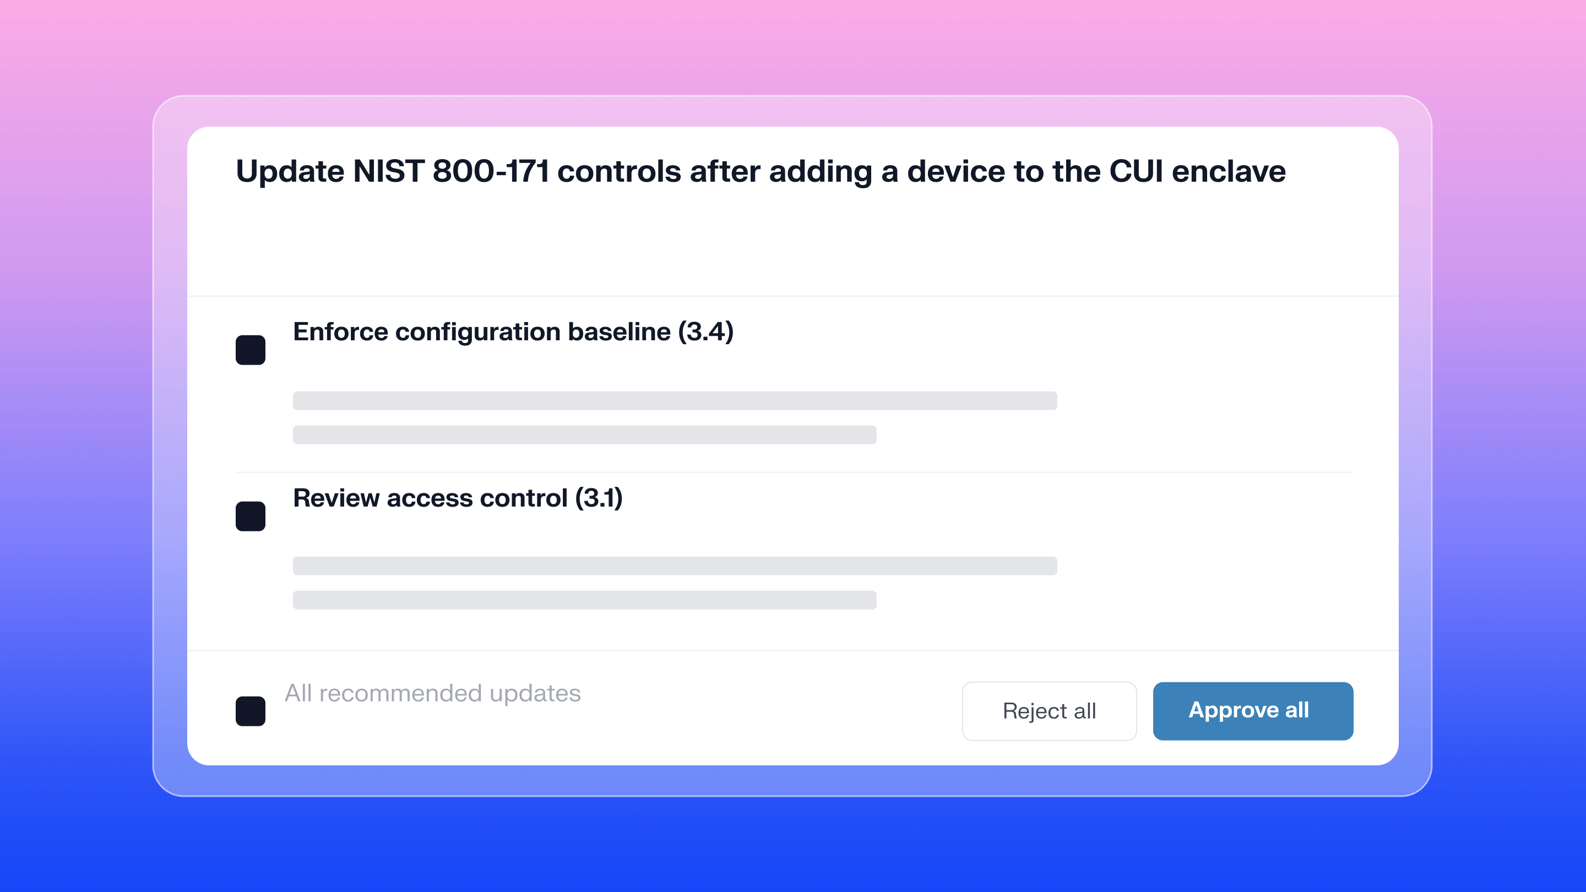
Iru's Adaptive Compliance capabilities watch for changes in your organization, and automatically suggest updates to your controls and actions.

  • Iru AI regularly checks for changes to your sources, artifacts or company profile
  • If a change is detected, a control update recommendation is surfaced for you to review, often within 24 hours
  • No changes are made without your approval, and every change is logged for your auditors to review
NIST 800-171 adaptive

Turn NIST 800-171 preparation into an always-on workflow

Iru's AI-powered compliance solution helps IT, security and GRC teams spend less time on manual compliance work and stay audit-ready all year.

Let your team focus 
on what matters

Iru replaces fragmented tools with one AI-powered platform, so IT & security spend less time chasing tickets and more time improving the business.

Frequently asked
questions

Get answers to commonly asked questions

Who publishes NIST 800-171, and who enforces it?

NIST publishes the standard. Enforcement, though, runs through contracts.

For defense work, DFARS clause 252.204-7012 requires contractors handling covered defense information to implement 800-171, and the requirement flows down to subcontractors. Verification of that implementation runs through CMMC

So NIST writes it, the Department requires it, and your prime contractor passes it down to you.

Which revision do we actually have to meet — Rev 2 or Rev 3?

Revision 2 is what you’ll have to meet for assessment purposes .

NIST published Revision 3 and marked Revision 2 as withdrawn on its website. But assessments are conducted against Revision 2 under a Department class deviation memo, and will continue to be until that memo is withdrawn or superseded. The Department has said Revision 3 will be incorporated through future rulemaking, without announcing a date.

You may implement Revision 3 voluntarily. If you do, you must use the Department's Organization-Defined Parameters, published in an April 2025 memorandum, rather than setting your own.

The practical advice: don't switch because NIST's website says Rev 2 is withdrawn. Check what your contract and your assessment require.

What changed in Revision 3?

The most structural change is three new requirement families, added for consistency with the SP 800-53B moderate baseline: Planning (PL), System and Services Acquisition (SA), and Supply Chain Risk Management (SR). Existing families also gained and lost individual requirements.

Revision 3 also introduced Organization-Defined Parameters — values the implementing organization sets — which is why the Department had to publish its own ODPs for contractors choosing to work to Rev 3 early.

What's the difference between NIST 800-171 and CMMC?

NIST 800-171 is the rulebook. CMMC is the inspection.

NIST 800-171 sets the security requirements — what you have to implement to protect CUI. CMMC is the Department's program for verifying you've done it, establishing levels, who can assess, and what has to be submitted.

They aren't interchangeable. CMMC Level 1 covers basic safeguarding of Federal Contract Information and isn't 800-171 at all. Level 2 is where the two essentially align. Level 3 goes further, drawing on the enhanced requirements in NIST 800-172.


And 800-171 isn't only a defense matter; civilian agencies reference it on contracts where CMMC doesn't apply.

What's the difference between NIST 800-171, NIST 800-53, and NIST CSF 2.0?

NIST 800-53 is the catalog — a comprehensive set of security and privacy controls, used by federal agencies and by organizations that need that depth. It's the source material the others draw on.

NIST 800-171 is derived from it. Its requirements are tailored from the 800-53 moderate baseline for nonfederal systems handling CUI. That's direct lineage rather than loose resemblance — Revision 3 added three new families specifically for consistency with the 800-53B moderate baseline. If you've implemented 800-53 at moderate, you've done much of 800-171 already.

NIST CSF 2.0 isn't a control set at all. It's an organizing framework built around Functions — Govern, Identify, Protect, Detect, Respond and Recover — that helps you structure a security program and talk about it with people who don't read control catalogs. It points at catalogs like 800-53 rather than replacing them. You don't implement CSF the way you implement 800-171.

And CMMC is none of the above — it's the Department's program for verifying that you've implemented 800-171.

Can we get "NIST 800-171 certified"?

No. NIST doesn't certify anyone, and there is no NIST credential to hold.

What exists is assessment. Depending on your contract, that's either a self-assessment — scored and submitted — or an assessment conducted by an authorized third party. The output is a score and a status, not a certificate from NIST.

If a supplier claims to be "NIST certified," ask what they actually mean: which revision, what level, self-assessed or third-party, and when.

Does this apply to us if we're a subcontractor?

Usually, yes. The DFARS safeguarding requirement flows down. If you handle covered defense information as part of a contract — at any tier — the obligation reaches you, and your prime will expect evidence of it.

Subcontractors are frequently the weakest link in a supply chain assessment, which is why primes have become considerably more demanding about seeing evidence rather than assurances.

Does SOC 2 or ISO 27001 cover NIST 800-171?

No. They overlap in evidence but answer different questions.

SOC 2 and ISO 27001 assess control criteria and management systems. NIST 800-171 is a prescriptive requirement set tied to a specific data type — CUI — and enforced through your contract rather than the market.

Much of the underlying evidence transfers. Access control, audit logging, configuration management, and incident response appear in all three. What doesn't transfer is the contractual obligation: a prime requiring NIST 800-171 will not accept a SOC 2 report instead.

Can Iru get us compliant with NIST 800-171?

No platform can make you compliant — that depends on your system boundary, your policies, your people, and an assessment you undergo.

What Iru does is the technical requirement families. The platform enforces access control and multi-factor authentication on the identities that reach CUI, maintains secure configuration across your devices, detects and contains incidents, manages media and device disposal, and keeps software patched — with the evidence collected continuously, so your assessment reflects current state rather than a snapshot taken the week before.

If you need an assessment, we can connect you with one of the assessors in our auditor network. Book a demo to explore the compliance solution, or if you're already a customer, reach out to your rep for details on our audit partners.

Stay up to date

Iru's bi-weekly collection of articles, videos, and research to keep IT & Security teams ahead of the curve.