Skip to content
When Great Engineers Quit: Why Tools Make or Break Job Satisfaction
Iru Team

•

7 min read

When Great Engineers Quit: Why Tools Make or Break Job Satisfaction

The tech industry has a retention problem, but not for the reasons most people expect. Rather than quitting because work is too complex or challenging, talented IT and security engineers tend to leave because their tools prevent them from doing meaningful work.

Thought Leadership
What WWDC 2025 and the Next macOS Release Could Mean for Apple Admins
Iru Team

•

6 min read

What WWDC 2025 and the Next macOS Release Could Mean for Apple Admins

Every year, Apple’s new macOS release offers an opportunity to innovate. It also brings uncertainty for IT teams trying to keep pace with constant change. With the next major release set to preview at WWDC 2025 (June 9 to 13), admins are preparing for a high-stakes upgrade cycle. Early previews hint at broad updates spanning the Apple product suite, from design changes that unify UX across devices to much-anticipated Apple Intelligence features.

Thought Leadership
Shadow IT: IT Professionals Adapt, Respond, and Redefine Control
Iru Team

•

7 min read

Shadow IT: IT Professionals Adapt, Respond, and Redefine Control

Shadow IT has always been a loaded term, typically implying rule-breaking, risk, or lack of control. But the reality is more nuanced. When we surveyed 115 IT professionals, what we found wasn’t a story of defiance. It was one of friction.

Reports
Dissecting the macOS 'AppleProcessHub' Stealer: A Technical Analysis
Christopher Lopez

•

14 min read

Dissecting the macOS 'AppleProcessHub' Stealer: A Technical Analysis

On May 15, 2025, the security research team MalwareHunterTeam (@malwrhunterteam) identified a suspicious file named libsystd.dylib with low detection—only 2 at the time of posting— which appeared to be an infostealer.

Threat Intelligence
Kandji Quarterly Threat Intelligence Report: May 2025
Alex Gartner

•

4 min read

Kandji Quarterly Threat Intelligence Report: May 2025

Welcome to the Iru Threat Intelligence Report, our quarterly summary of emerging threats in the macOS ecosystem and how Iru is responding in real time. In each edition, we break down key threat discoveries and the protections we’ve deployed to keep customer devices secure.

Threat Intelligence
macOS Vulnerabilities: A Year of Security Research at Iru
Alex Gartner

•

10 min read

macOS Vulnerabilities: A Year of Security Research at Iru

Iru security researchers have been hard at work hunting for vulnerabilities in macOS, reporting them to Apple before malicious actors can exploit them. This proactive approach is a cornerstone of our product strategy, benefiting not just our customers but the entire Apple ecosystem.

Threat Intelligence
PasivRobber: Chinese Spyware or Security Tool?
Nick Zolotko, Christopher Lopez, & Adam Kohler

•

28 min read

PasivRobber: Chinese Spyware or Security Tool?

On March 13, 2025, our team found a suspicious mach-O file on Virustotal named wsus. After our initial analysis of this file and the package which installed it, we discovered over 20 related binaries used to capture data from macOS systems and applications, including WeChat, QQ, web browsers, email, etc. This multi-binary suite indicates a deep understanding of macOS and their target applications. The software’s targeted applications and other observed network connections strongly indicate both a Chinese origin and target user base.

Threat Intelligence
Survey Results: The Top Content and Communities for IT & Security Pros
Iru Team

•

11 min read

Survey Results: The Top Content and Communities for IT & Security Pros

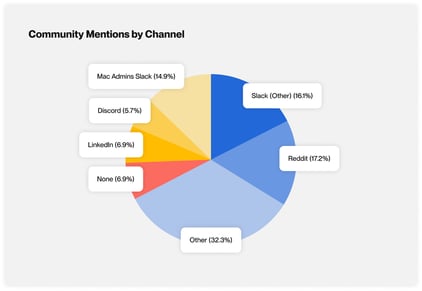
Are you curious where your peers get updates on the latest IT and security news? Or maybe you have an inside scoop on a resource or conference that deserves more recognition? We were curious, too. So, we took the question to our community in a broad survey of professionals - from security experts to technology leaders and admins. The responses gave us great insights into where IT and security practitioners are hanging out online and in-person, including the top:

Reports
Caught in the WebKit: Getting Tangled with CVE-2025-24201
Shwena Kak & Candace Jensen

•

4 min read

Caught in the WebKit: Getting Tangled with CVE-2025-24201

Web browsers are the gateway to the internet, a ubiquitous fixture of every enterprise device—making them a critical point of exposure. When managing your fleet you may ask: Are we aware of the vulnerabilities affecting our users’ browsers? While vulnerability databases are a great place to start, the widespread use of common codebases makes it harder to trace and recognize vulnerabilities that affect multiple products.

Threat Intelligence
Uncovering Apple Vulnerabilities: diskarbitrationd and storagekitd Audit Part 3
Csaba Fitzl

•

10 min read

Uncovering Apple Vulnerabilities: diskarbitrationd and storagekitd Audit Part 3

Over the past two parts of this series, we’ve explored vulnerabilities in macOS’s diskarbitrationd daemon. In part 1, we explored how an attacker could use it to escape the sandbox or escalate privileges. In part 2, we explored how a directory traversal attack could be used to bypass Transparency, Consent, and Control (TCC) protections. Each of these vulnerabilities highlighted the risks posed by weaknesses in macOS’s system daemons and how attackers could chain them together for even more impact.

Threat Intelligence
DPRK DriverEasy & ChromeUpdate Deep Dive
Christopher Lopez

•

16 min read

DPRK DriverEasy & ChromeUpdate Deep Dive

Over the last few months, several Swift applications have been attributed to the North Korea Contagious Interview effort. These applications are presented to victims as part of a fake job interview process. SentinelOne recently published a blog post on “Flexible Ferret” and other related applications including two named ChromeUpdate (which was originally covered by dmpdump in their blog post) and CameraAccess. Moonlock Lab also recently covered the ChromeUpdate and CameraAccess applications in a blog post, which provided an overview of what they do.

Threat Intelligence
Vulnerability Management: First Unified Platform to Detect & Remediate on Mac
Matt Day

•

4 min read

Vulnerability Management: First Unified Platform to Detect & Remediate on Mac

With attackers exploiting vulnerabilities three times more frequently than last year, managing vulnerabilities across a Mac fleet requires comprehensive visibility and timely action. Today, the Iru team is excited to announce Iru Vulnerability Management, which helps IT and security teams identify and remediate vulnerabilities through a unified workflow.

Product News
Banshee Rust Rewrite?
Christopher Lopez

•

9 min read

Banshee Rust Rewrite?

Infostealers targeting macOS are evolving rapidly, making continuous monitoring essential, which our team is always on the lookout for. Many infostealers share similar behaviors aimed at exfiltrating data from compromised systems. In fact, these similarities can make it difficult to distinguish between different infostealers without a deep understanding of what to look for.

Threat Intelligence
How to Manage Activation Lock: A Guide for Apple Admins
Mike Boylan

•

10 min read

How to Manage Activation Lock: A Guide for Apple Admins

Activation Lock is a theft-deterrent feature found in iOS and iPadOS devices and modern Mac computers (with the Apple T2 Security chip and Apple silicon). When such a device is attempted to be set up after having been erased, it checks with Apple servers to see if Activation Lock is on. If it is, the device requires the user’s Apple Account password before it can be used again (reactivated). This effectively removes the device’s resale value, making it less attractive to thieves.

Thought Leadership
Potential Stealer: Purrglar in Progress
Christopher Lopez & Nick Zolotko

•

28 min read

Potential Stealer: Purrglar in Progress

Unlike traditional viruses or ransomware, stealers are designed with a singular purpose: to quietly infiltrate systems and exfiltrate sensitive data—often without the victim even realizing it. These malicious programs are highly focused on gathering personal information, usually to be sold or used for further criminal activity.

Threat Intelligence

Stay up to date

Iru's bi-weekly collection of articles, videos, and research to keep IT & Security teams ahead of the curve.